Reduce Software Supply Chain Risk. Validate supplier SBOMs. Understand what is really inside your products. Hunt for the risks they may not reveal
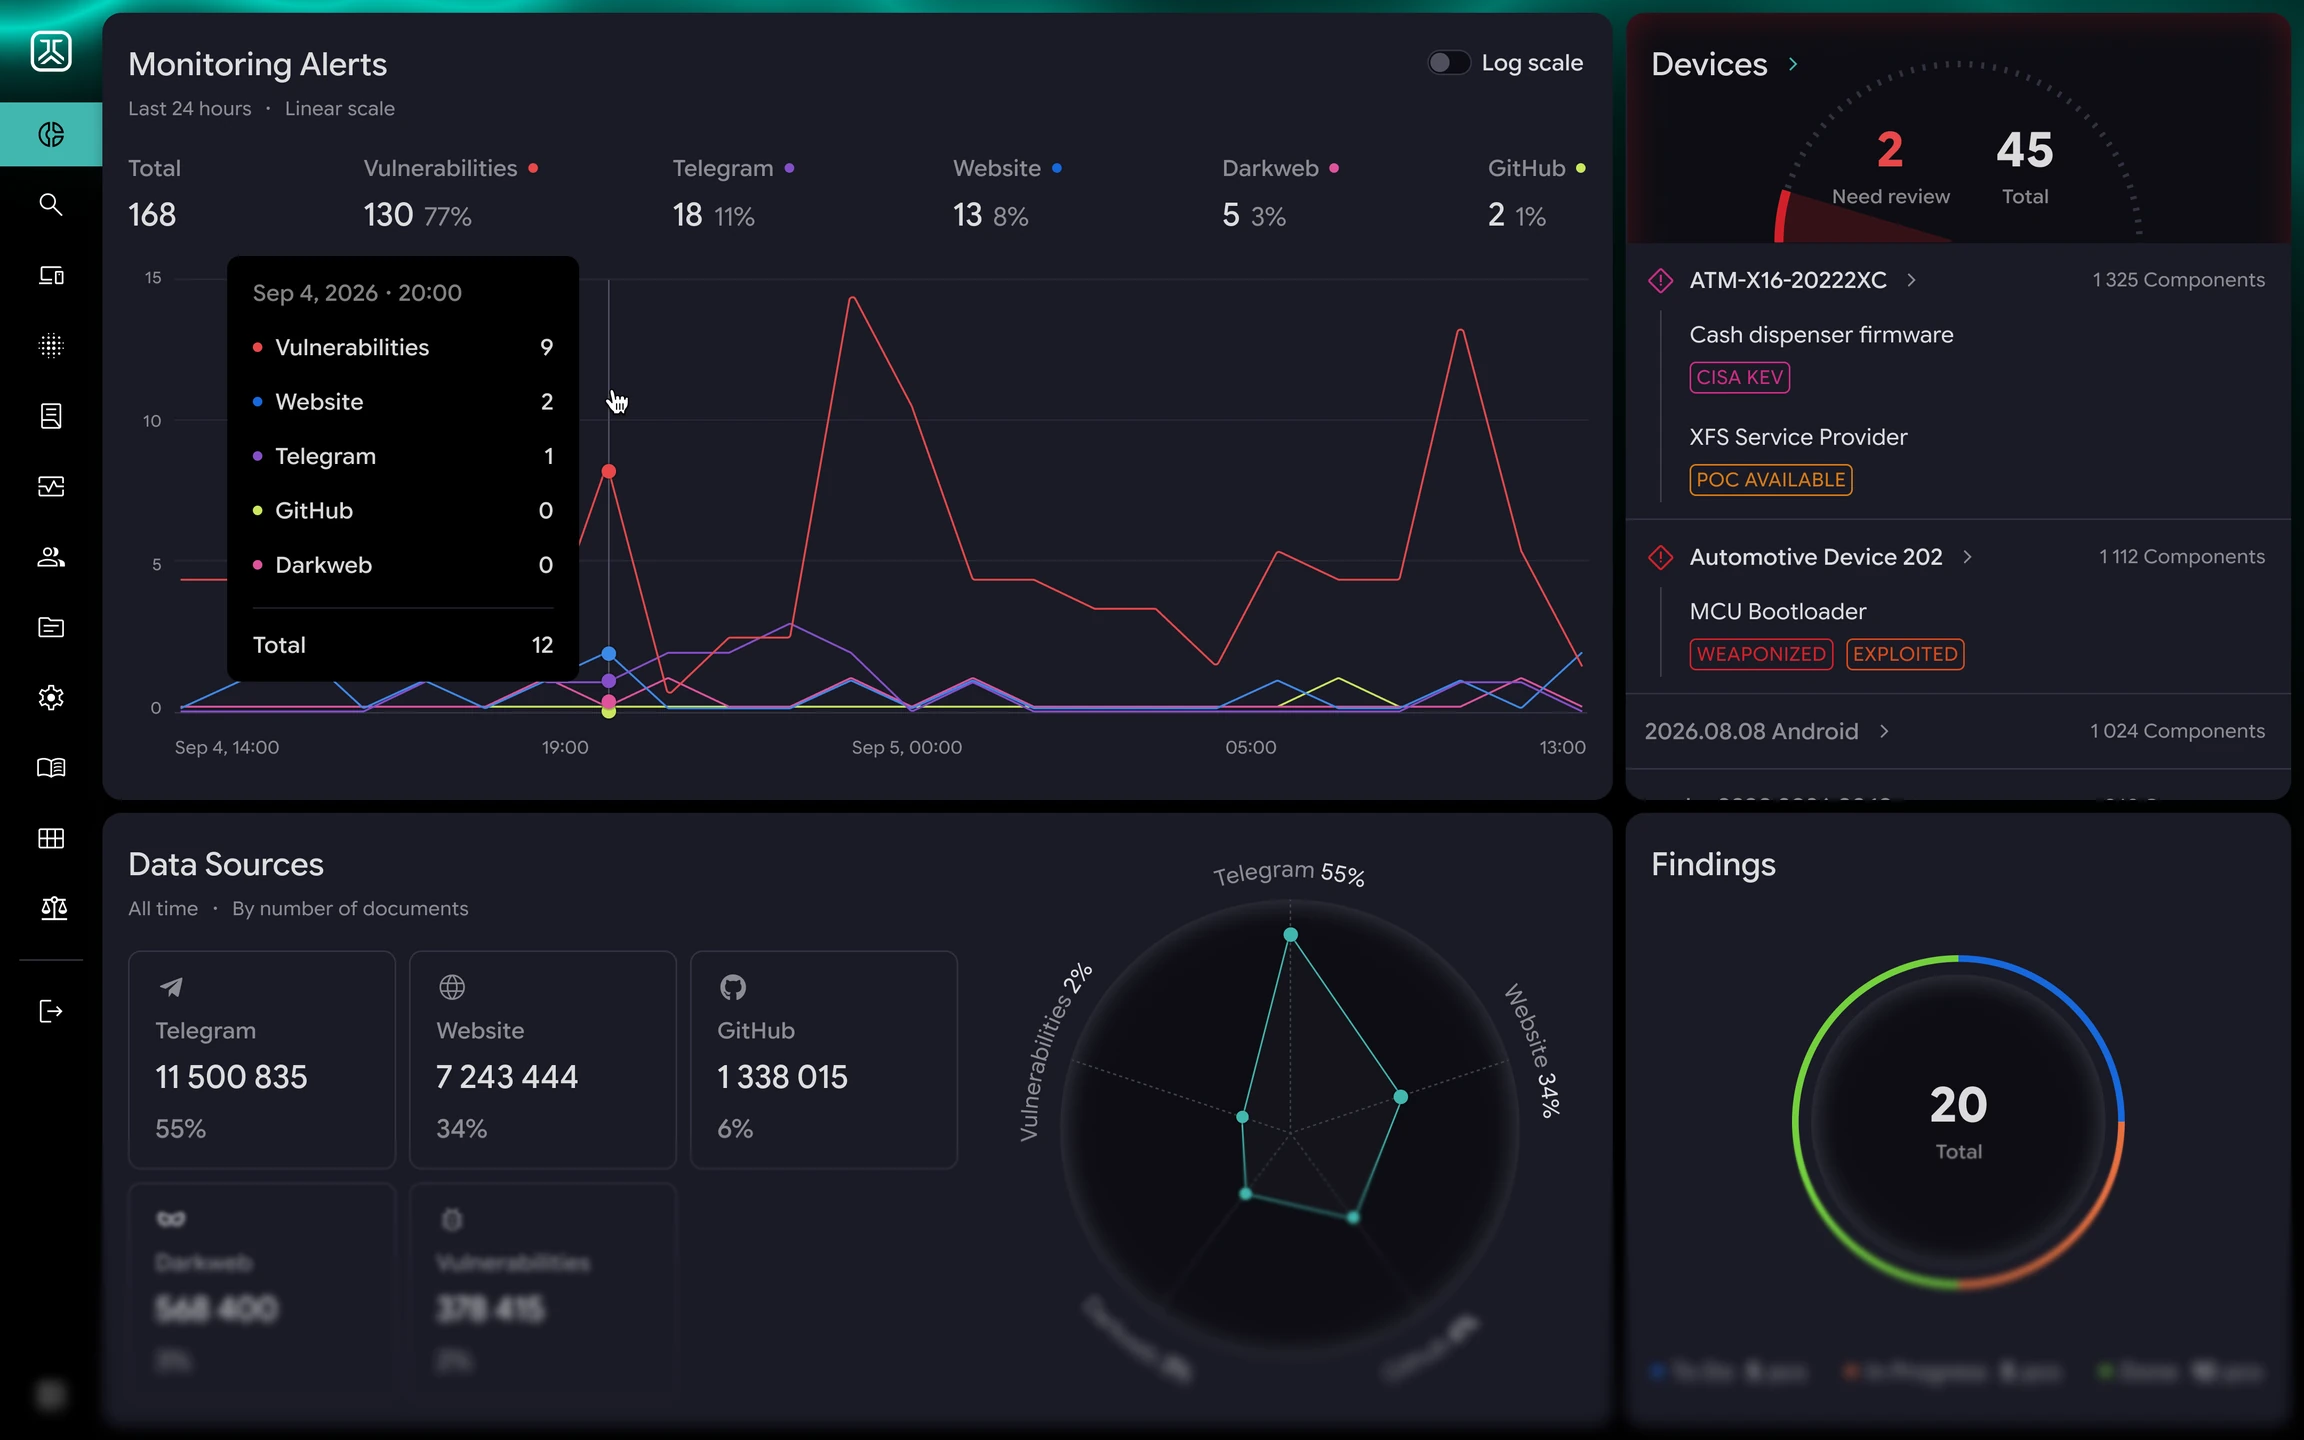
PCA CERVUS combines SBOM analysis, device-centric vulnerability intelligence, threat hunting and
deep/dark web monitoring to give you a broader view of software supply chain risks
Don't simply trust the SBOM
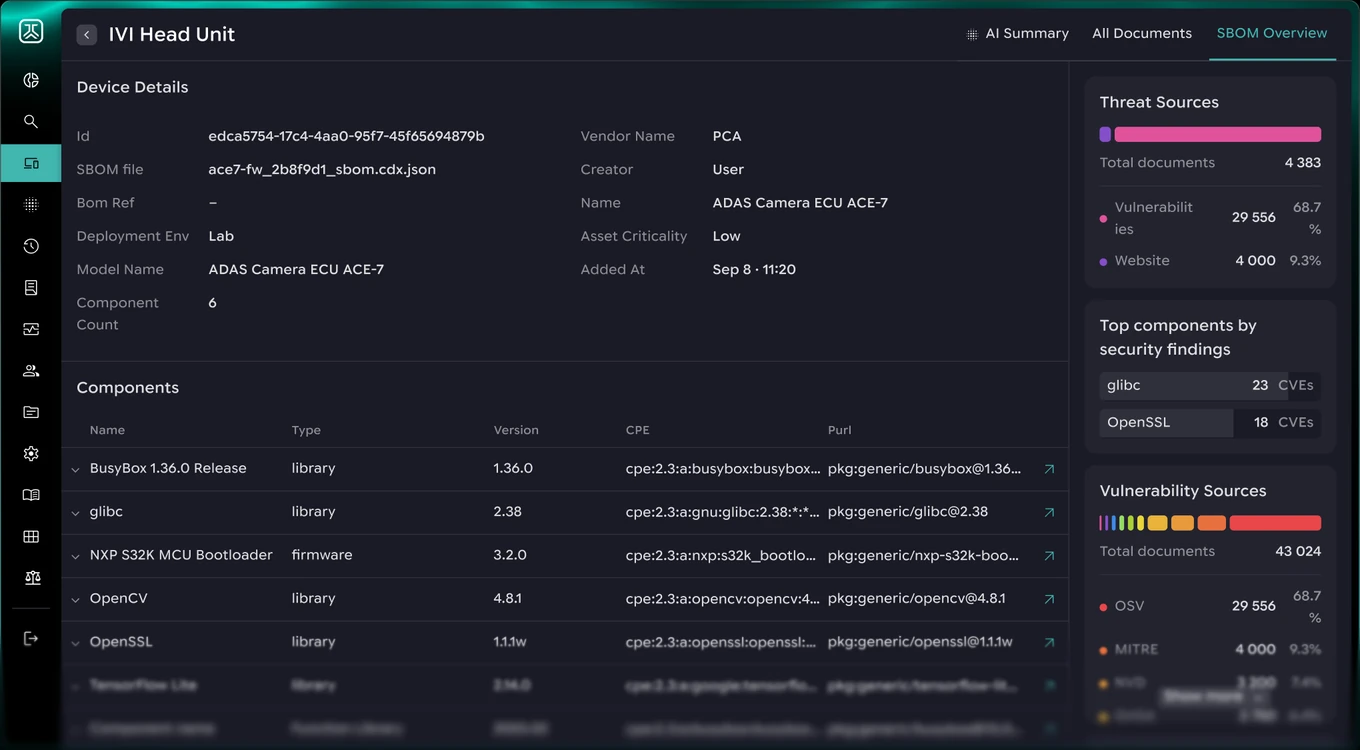
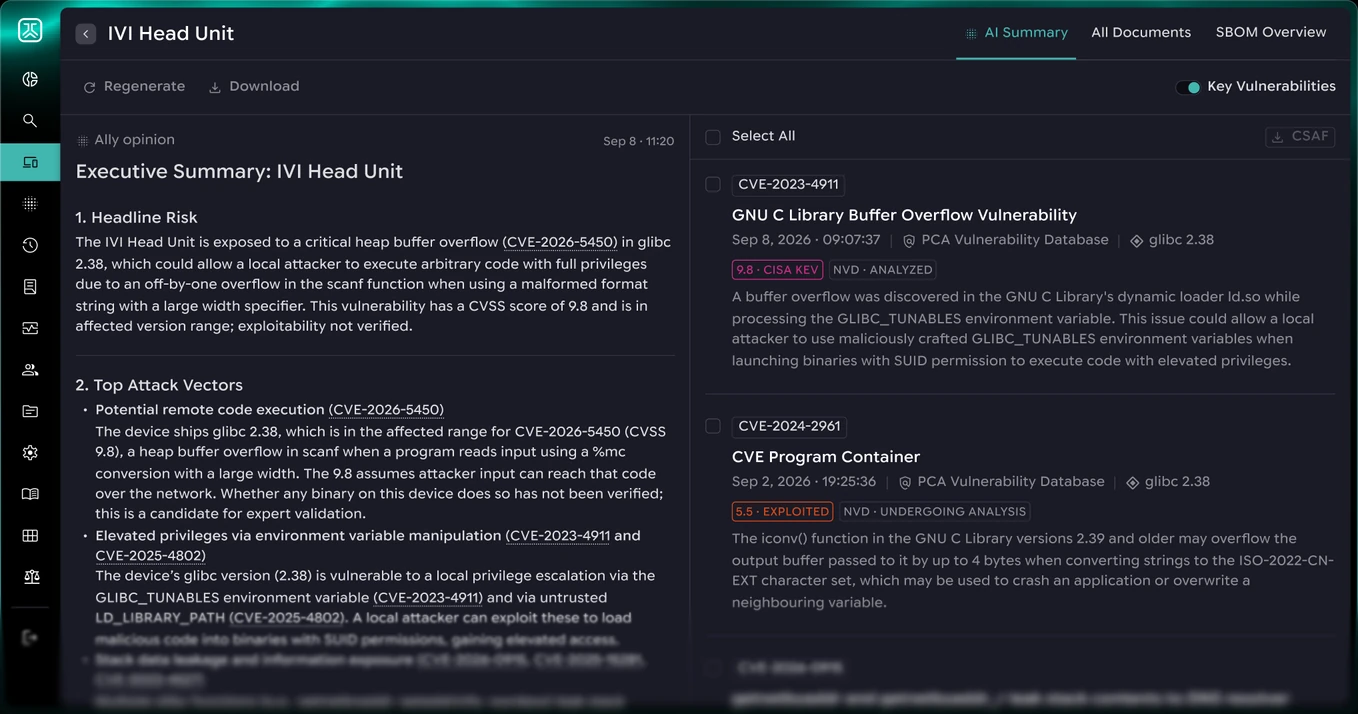
An SBOM is only useful when it accurately represents the actual software components with all their dependencies in your product. PCA CERVUS combines SBOM analysis with vulnerability intelligence and PCA's embedded security expertise to identify potential gaps, inconsistencies and risks.
Look beyond component names
Embedded software often contains components, versions and dependencies that are difficult to map against conventional vulnerability databases. PCA CERVUS helps connect your software inventory with relevant vulnerability intelligence and highlights where further investigation may be needed.
Hunt beyond conventional databases
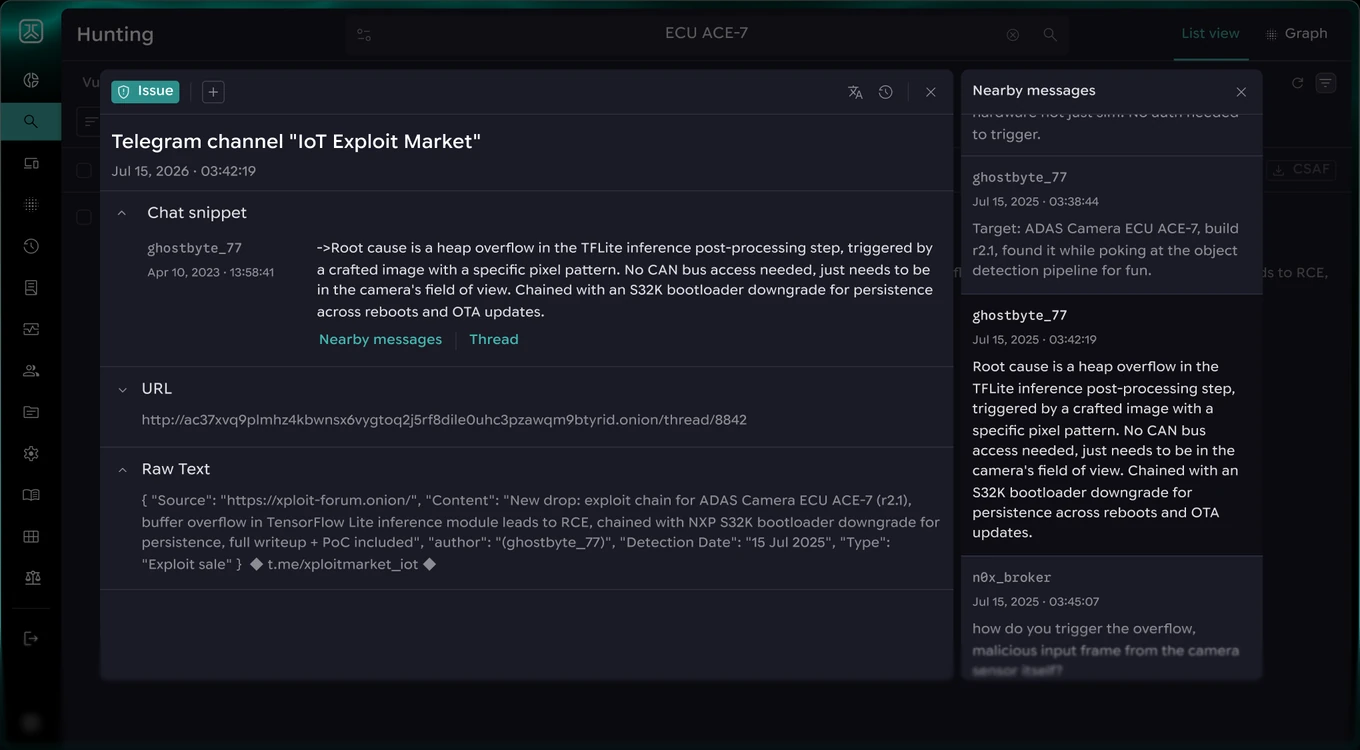
PCA's threat intelligence analysts supported by PCA CERVUS investigate exploit activity, threat actor discussions and other signals that can provide additional context around emerging component risks.
Monitor the wider threat landscape
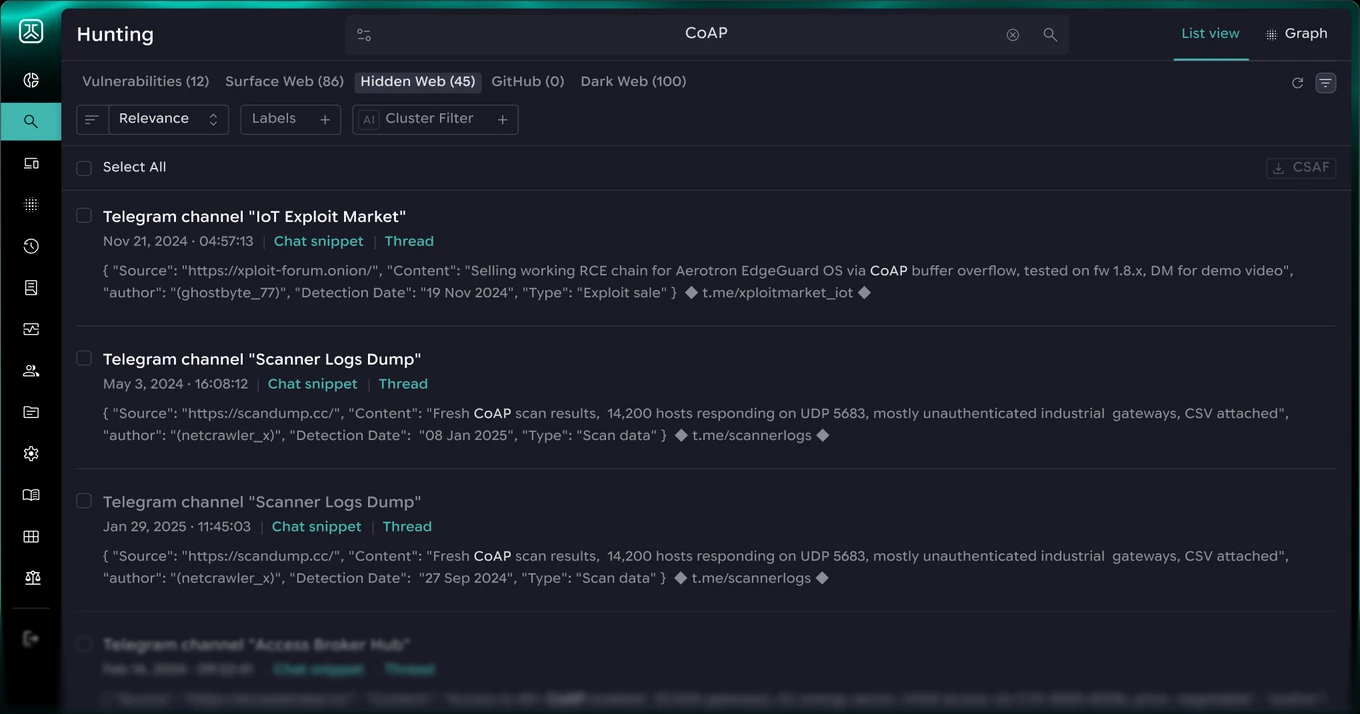
With deep web and dark web monitoring PCA CERVUS can surface leaked credentials, data, technical information or discussions that may indicate risks connected to your products, suppliers or technologies.
Make supplier risk visible
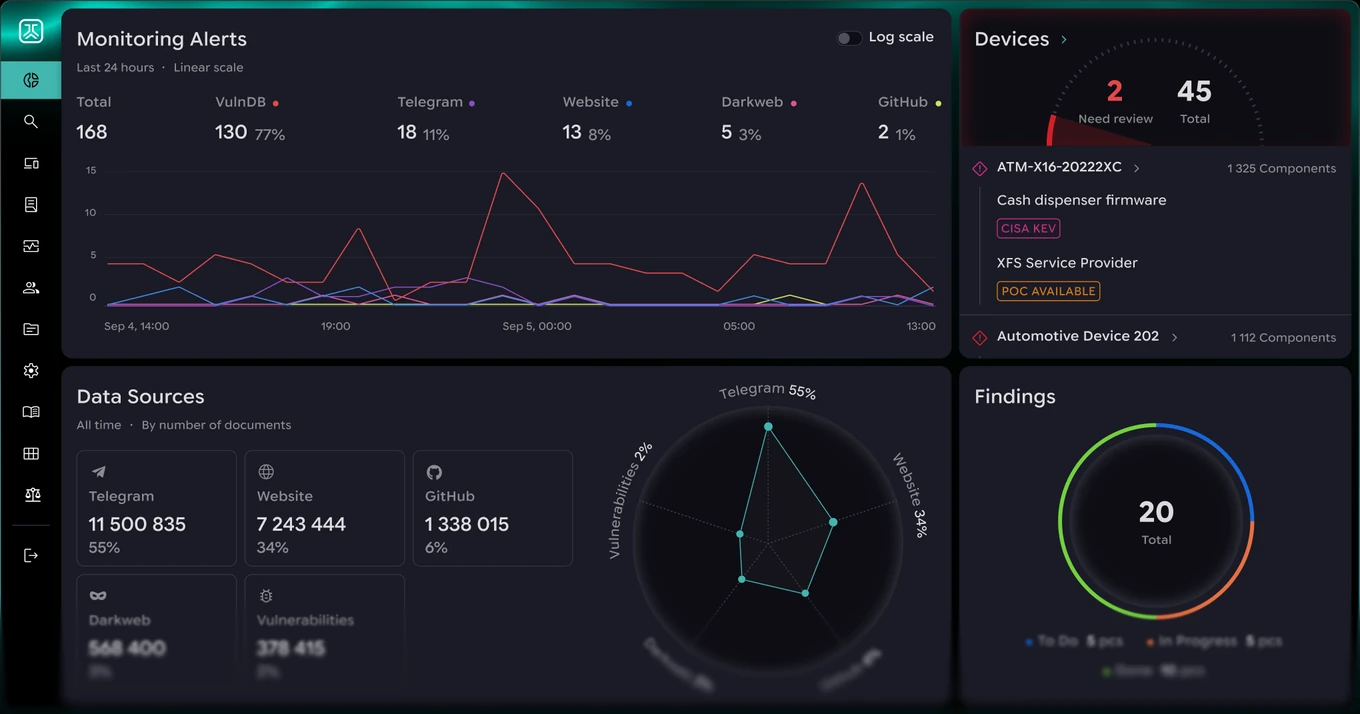
Assess incoming SBOMs, identify vulnerabilities and generate actionable intelligence for your product security and supplier management teams. The findings will be adapted to your existing ticketing system and provided in a customized format.
Questions? We have answers
PCA CERVUS is a device-centric, unified, embedded-focused Vulnerability Monitoring & Threat Intelligence platform that helps product security teams continuously identify device risks, validate and/or generate SBOMs, prioritize vulnerabilities with threat intelligence, and support compliance with evolving regulations such as Cyber Resilience Act, PCI DSS, PCI PTS, RED and UNECE R155.
PCA CERVUS helps organizations continuously discover, assess, prioritize and monitor security risks throughout the product lifecycle – from development and certification through deployment and maintenance.